Secure network connections with IPsec

IP packets, the fundamental unit of internet data transfer, consist of two parts: the actual payload (voice, text, images) and header data containing sender and recipient addresses. The core problem: IP itself provides no confidentiality or authentication at the network layer – regardless of any application-level encryption the payload may already carry. Without additional mechanisms, packets can be read or manipulated in transit, leaving three security properties unprotected: confidentiality, integrity, and authentication (the security services defined in the IPsec architecture, RFC 4301).
IPsec (Internet Protocol Security) was developed to close this gap. The protocol suite operates at the network layer and secures IP communications independently of the application being used – which is why it remains the backbone of most site-to-site VPN connections today.
What is IPsec?
IPsec is a protocol suite standardized by the Internet Engineering Task Force (IETF). Early IPsec specifications (from RFC 1825, 1995, onward) addressed both IPv4 and IPv6. The key distinction today is that IPsec support is mandatory for IPv6 (RFC 6434) and optional for IPv4, where it is deployed as an add-on. In practice, IPsec is widely used in both protocol versions. The suite divides into three functional groups:
- Transfer protocols: Authentication Header (AH, RFC 4302), Encapsulating Security Payload (ESP, RFC 4303)
- Key management: Internet Key Exchange v2 (IKEv2, RFC 7296); ISAKMP (RFC 2408, now Historic) is a legacy predecessor used with IKEv1
- Databases: Security Association Database (SAD), Security Policy Database (SPD) – defined in the IPsec architecture RFC 4301
- NEW: Flexible scaling with VM-cloning, load balancing, new storage options and more
- Unlimited traffic and >99.99% availability
- 24/7 expert support and your own personal consultant
Components of the protocol suite
The two main transfer protocols differ significantly in what they protect and how:
ESP (Encapsulating Security Payload) is the standard for all modern IPsec deployments. It provides encryption, authentication, and integrity protection in one header. When used with an AEAD cipher like AES-GCM, ESP handles encryption and authentication in a single pass – no separate HMAC calculation is needed.
AH (Authentication Header) provides integrity and origin authentication only – but no encryption. More critically, AH authenticates the entire packet including the outer IP header, making it incompatible with NAT – a problem in virtually every modern network. ESP with authentication achieves equivalent protection and works through NAT. Current BSI (TR-02102-3) and NIST guidelines recommend ESP exclusively; AH is considered effectively obsolete.
ESP protects data through four mechanisms:
- Confidentiality – payload content is encrypted
- Integrity – any tampering in transit is detected
- Origin authentication – confirms the packet came from the expected peer
- Replay protection – each packet carries a monotonically increasing sequence number; the receiver maintains an anti-replay window and rejects any packet whose number falls outside the window or has already been processed
SAD and SPD
The Security Policy Database (SPD) defines which traffic should be protected and with which protocol. The Security Association Database (SAD) holds the active session parameters negotiated by IKEv2: for each SA, the SAD stores the Security Parameter Index (SPI), the chosen algorithms, and the associated key material. Each SA is unidirectional – a single protected connection therefore requires two SAs, one per direction, each with its own SPI and keys.
IKEv1 vs. IKEv2
IKEv2, standardized in RFC 7296 (2014), is the current key management standard for IPsec. IKEv1 (RFC 2409, 1998) is deprecated and should not be used in new deployments – it has known cryptographic weaknesses, a complex handshake, and lacks features standard in modern implementations. If your VPN gateway still defaults to IKEv1, update the configuration.
IKEv2 redesigned the handshake from the ground up and adds several critical capabilities over IKEv1:
- Simpler handshake: always 4 messages (IKEv1 Main Mode required 6–9)
- Built-in NAT traversal: automatic ESP-in-UDP encapsulation on port 4500 when NAT is detected
- MOBIKE (RFC 4555): allows a tunnel to survive an IP address change without renegotiating – essential for devices switching between Wi-Fi and cellular networks
- EAP authentication: native support for certificates, pre-shared keys, and EAP
- Dead Peer Detection: built in via INFORMATIONAL exchanges (IKEv1 required a separate extension)
- Perfect Forward Secrecy: configurable per child SA – ensures past sessions cannot be decrypted even if a long-term key is later compromised
The two types of IPsec: Tunnel vs. Transport
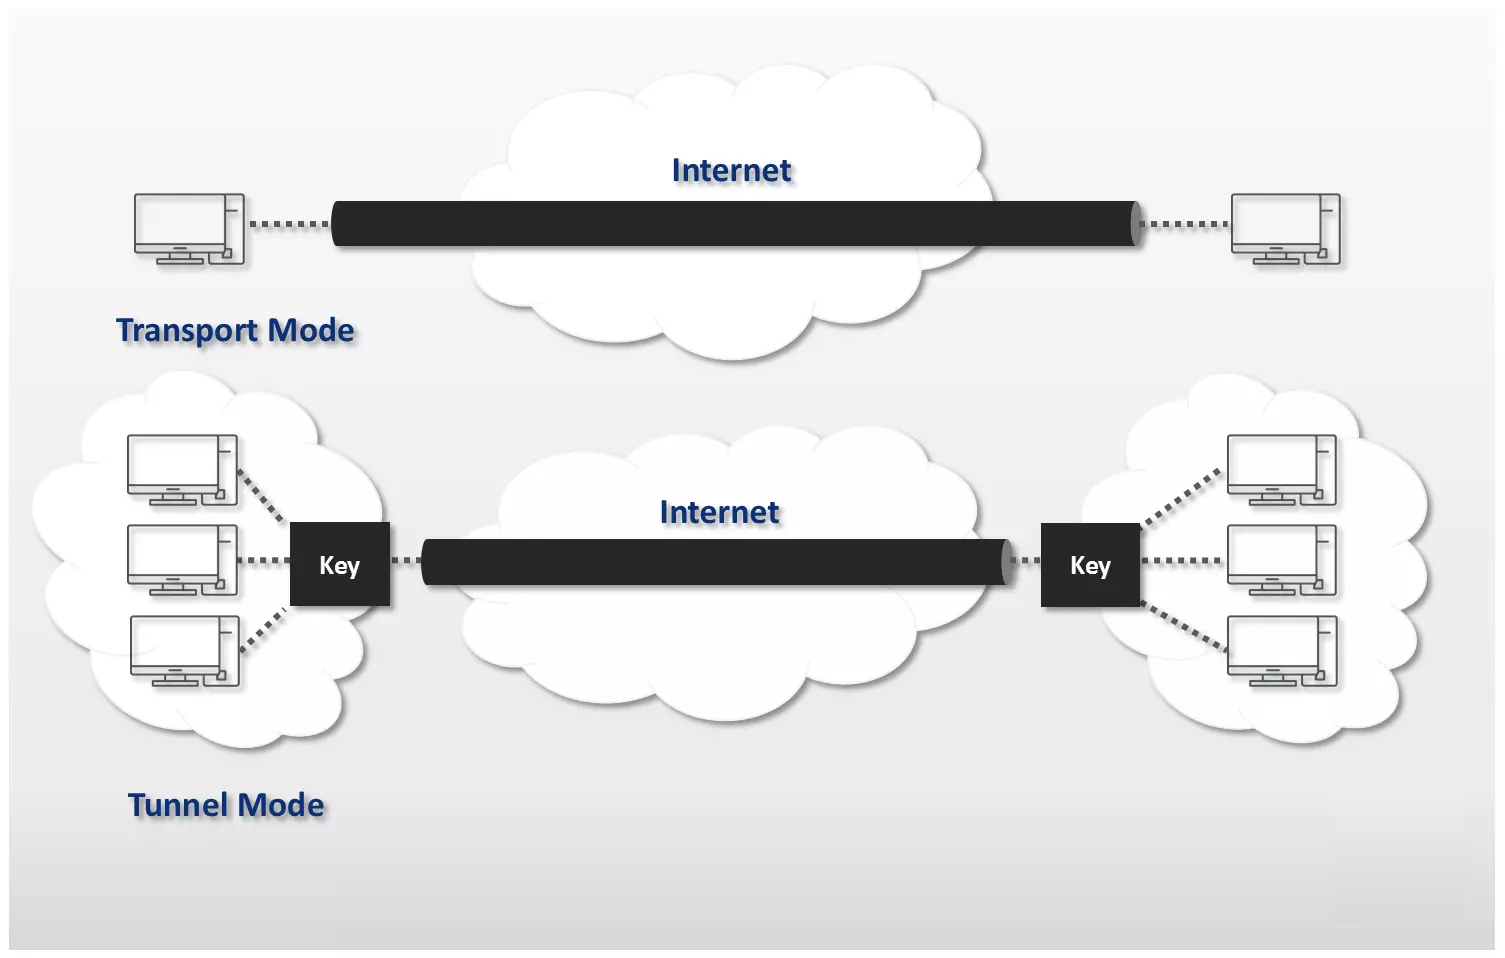
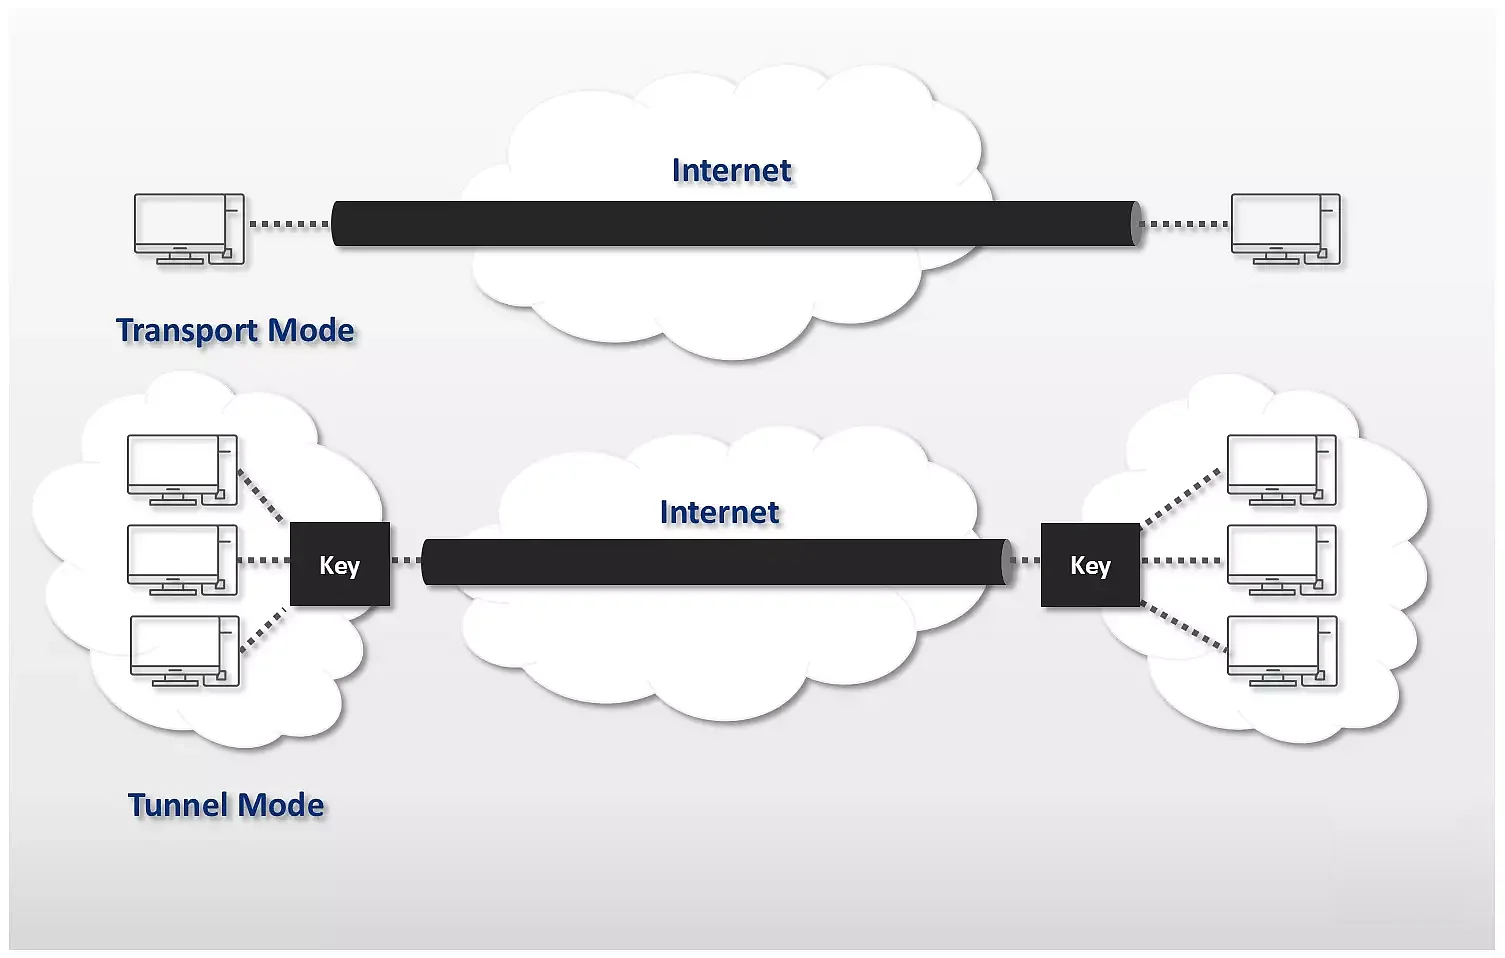
There are two existing transfer modes for secure connections with IPsec: transport mode, in which two end hosts are connected directly, and tunnel mode, which creates a connection between two IP networks.
Transport mode
In transport mode, IPsec inserts its headers between the existing IP header and the payload. The original IP header – including source and destination addresses – remains visible. Only the payload is protected. This mode is efficient and fast, but does not conceal the communicating endpoints. The cryptographic and communicative terminal points are identical.
Typical use: host-to-host connections, network management traffic, and as the inner tunnel in L2TP/IPsec configurations for remote access clients.
Tunnel mode
In tunnel mode, the entire original IP packet is encapsulated inside a new packet with a new outer IP header. Both the payload and the original header (with the real source and destination addresses) are hidden inside the encrypted ESP payload – only the gateway addresses are visible in transit.
Typical use: site-to-site VPNs (gateway to gateway) and road warrior VPN clients where endpoint identity must be concealed. When IKEv2 detects NAT in the path during its handshake, it automatically encapsulates ESP inside UDP on port 4500, allowing IPsec tunnels to pass through routers and firewalls that would otherwise drop raw ESP packets (IP protocol 50).
Cipher suites and security recommendations
Choosing the right algorithms is as important as deploying IPsec correctly. The following is aligned with BSI Technical Guideline TR-02102-3 (2024) and current NIST recommendations.
Encryption (ESP):
- AES-256-GCM – Recommended. Authenticated encryption (AEAD) – no separate HMAC needed. Hardware-accelerated via AES-NI on modern CPUs.
- AES-128-GCM – Acceptable for most deployments.
- AES-256-CBC – Acceptable if combined with HMAC-SHA-256 or SHA-384. Avoid without separate authentication.
- 3DES / DES – Do not use. Deprecated by NIST (2023). Vulnerable to the Sweet32 attack (3DES) or trivially broken (DES).
Integrity / Authentication (for non-AEAD ciphers):
- HMAC-SHA-256 – Minimum recommendation.
- HMAC-SHA-384 / SHA-512 – Preferred for high-security environments.
- HMAC-MD5 / HMAC-SHA-1 – Do not use.
Key exchange – IKEv2 Diffie-Hellman groups:
- Group 19 (P-256 / ECDH) – Recommended default.
- Group 20 / 21 (P-384 / P-521) – Higher security margin for sensitive deployments.
- Group 14 (2048-bit MODP) – Minimum acceptable; only for legacy compatibility.
- Groups 1, 2, 5 (768–1536-bit) – Do not use. Considered broken.
Looking ahead: Post-quantum cryptography
Quantum computers capable of breaking current asymmetric key exchange are not yet operational, but the IETF is already preparing the transition. RFC 9370 (2023) defines multiple key exchanges in IKEv2, enabling hybrid classical/post-quantum key agreement. NIST finalized its first post-quantum algorithm standards in 2024 (FIPS 203, 204, 205). High-security and long-lifecycle deployments should monitor BSI and NIST guidance on migration timelines.
IPsec: strengths and weaknesses
When using VPNs – the most common application area of the protocol suite – IPsec operates independently from any application at network level. Once the connection is made, different forms of data (e-mail, file transfer, IP telephony) can be sent without application-specific tools. It scales to thousands of simultaneous tunnels, is supported natively by major operating systems, and benefits from widespread hardware acceleration (AES-NI).
The trade-offs: IPsec is complex to configure correctly, and misconfiguration is a genuine risk. Its large codebase is difficult to audit fully. Devices that still ship with IKEv1 or weak ciphers enabled by default require manual hardening.
Comparison with modern alternatives:
- IPsec / IKEv2 (network layer): best for site-to-site VPNs, enterprise environments, and mobile clients – mature, scales well, complex configuration.
- SSL / TLS VPN (application layer): best for remote access and clientless browser-based scenarios – easier firewall traversal, per-app tunneling.
- WireGuard (network layer): a modern alternative integrated into the Linux kernel since version 5.6 (2020). Its minimal codebase (~4,000 lines) makes it significantly easier to audit and it consistently outperforms IPsec in benchmarks on constrained hardware. WireGuard uses a fixed, modern cipher suite (ChaCha20-Poly1305, Curve25519) and is worth evaluating for greenfield Linux deployments. It lacks the enterprise feature set and vendor interoperability that IPsec provides.
Use cases
Site-to-site VPN: The most common IPsec deployment. Two network gateways establish a permanent tunnel in tunnel mode, encrypting all traffic between two office or datacenter networks. IKEv2 handles key exchange and re-keying; ESP with AES-256-GCM encrypts the payload. Dead Peer Detection automatically re-establishes the tunnel if a peer becomes unreachable.
Remote access (road warrior): IKEv2/IPsec combined with EAP authentication allows individual users to connect securely from laptops and mobile devices. MOBIKE ensures the tunnel persists when the device’s IP address changes – for example, when switching from a hotel Wi-Fi to a cellular connection. Windows, macOS, iOS, and Android all include a native IKEv2 client, requiring no third-party software installation.
Host-to-host (transport mode): Used for securing traffic between specific servers – database replication, inter-datacenter synchronization, or management plane communication – without routing through a gateway. Transport mode adds minimal overhead but requires IPsec policy configuration on both endpoints.
Reviewer
Christian Heldmaier
Christian Heldmaier is an experienced online marketing and SEO specialist from Karlsruhe. He has been working as an SEO Manager at IONOS since July 2020.